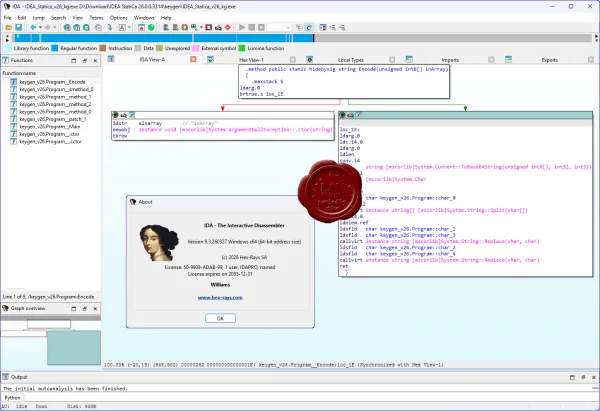
Klik gambar untuk perbesar
Produk Digital
Hex-Rays IDA Pro Advanced
Belum ada ulasan ·
9 dilihat
Rp 77.500
Rp 350.000 -78%
PO 1 Hari Diproses penjual, dikirim maks 24 jam.
Pembayaran QRIS terverifikasi otomatis. Link download otomatis setelah lunas (email/WhatsApp).
Deskripsi
Build 260327 IDA Pro is one of the most famous professional disassemblers and reverse engineering tools. It is used by information security specialists, malware researchers, and developers who need to analyze already compiled programs without source code. Main features of IDA Pro Disassembly. IDA Pro automatically converts binary files (EXE, DLL, ELF, etc.) into assembly code, taking into account the processor architecture (x86, ARM, etc.) Interactive analysis. Unlike simple disassemblers, IDA builds function graphs (control flow graph), recognizes functions, loops, transitions, and allows you to rename variables and functions. Decompilation. With the Hex-Rays Decompiler plugin, you can get pseudocode in a C-like language, making analysis much easier. IDA has a built-in debugger. You can run the program step by step, look at the register values.
Ulasan Produk
- dari 0 ulasan
Masuk dan beli produk ini untuk memberi ulasan.
Belum ada ulasan. Jadilah yang pertama!